PRODUCTS
Packet Capture & Analytics
Capture every packet.
Solve problems faster.

Capture every packet.
Solve problems faster.
Network incidents don’t wait for troubleshooting tools to start collecting data. cPacket automatically captures, indexes, and analyzes every packet at line rate – nothing sampled, nothing lost. Continuous capture enables real-time network performance and security monitoring, while preserving the evidence NetOps and SecOps teams need to investigate past issues.
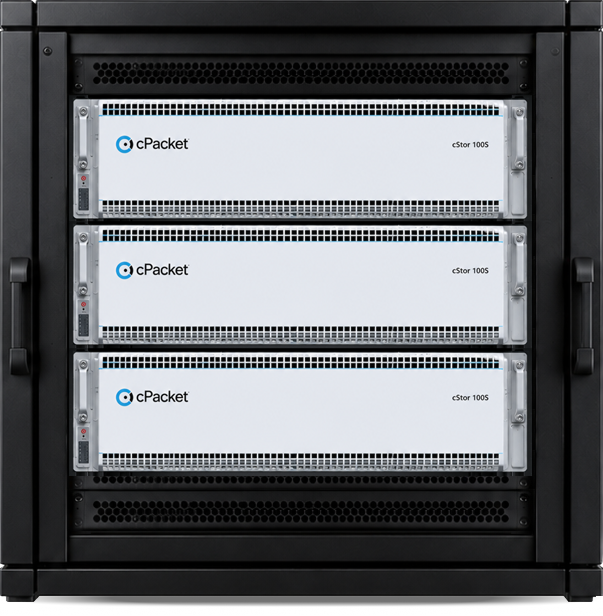
Available as physical and virtual appliances, cStor packet capture appliances combine powerful compute, storage, and networking to support the most demanding networks. Just as important are cPacket’s real-time analytics, which provide engineers with session metrics and application-level insights to detect and identify the cause of incidents.
Use unsampled network traffic as the source of truth for troubleshooting and forensic analysis.

Query and analyze stored traffic while new packets continue flowing to disk.
Scale raw storage beyond 2800 TB for longer investigation and compliance windows.

Capture traffic across physical, virtual, and cloud environments with a consistent operational experience.

Continuously capture every packet at sustained rates from 10 Gbps to 200 Gbps.
Organize and tag packets during capture so engineers can quickly query, retrieve, and analyze relevant traffic.

Analyze TCP sessions, flows, Layer-7 protocols, multicast market data and video, and other protocols to monitor performance, capacity, latency, and errors.
Merge captures, replay packets, and inspect raw PCAP data with integrated Wireshark while capture continues.
Get answers to common questions about network observability and cPacket solutions.
cStor appliances records every packet traveling across network to persistent storage, indexes them for retrieval and generates analytics for real-time and historical investigation.
No. It automatically captures every packet at line rate, providing complete data for troubleshooting, performance analysis and security investigations.
Yes. Simultaneous reading and writing provide access to stored packets without stopping ongoing capture and indexing.
cStor packet capture appliances support TCP and flow analytics, Layer-7 analytics (including HTTP/HTTPS, DNS, SIP, RTP, and others), as well as multicast video analysis and financial market data analytics.
It is available as cPacket hardware and as a virtual appliance for industry-standard servers and major cloud environments, including AWS, Google Cloud, and Microsoft Azure.
Our team of experts can work with you to align your network strategy to cPacket’s industry-leading packet broker and capture solutions.